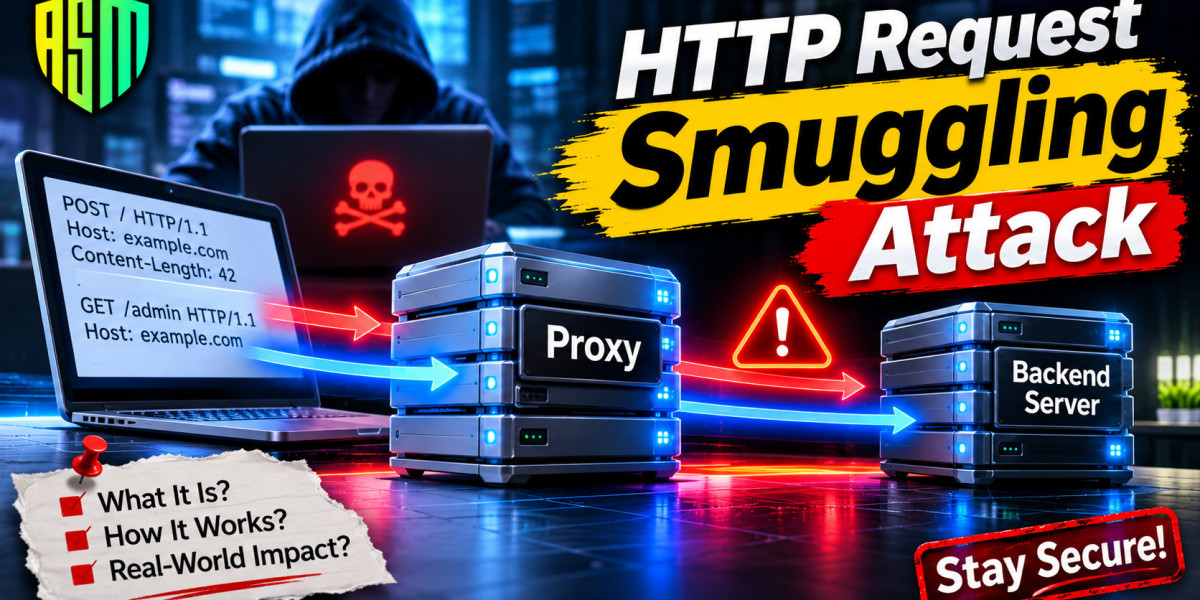

Once a tester confirms an HTTP Request Smuggling vulnerability exists, exploitation moves from there a desync here to here is what an attacker does with it. The main techniques are response queue poisoning, bypassing frontend access controls, hijacking another user's session or request and poisoning shared caches. Each technique targets a different piece of trust the front end was supposed to enforce and each requires a slightly different crafted payload once the underlying CL.TE, TE.CL, or TE.TE condition is confirmed.
Finding an HTTP Request Smuggling Attack vulnerability and exploiting one are two different skill sets. A timing based probe tells you a desync condition exists. Turning that condition into a demonstrable, reportable impact on the part that actually matters to a client or a bug bounty triager requires understanding what you are actually trying to build with the smuggled bytes. This guide walks through the exploitation techniques themselves, organized by attacker goal rather than by vulnerability variant, since that's the order most testers actually think in during a live engagement.
From Confirmed Desync to Working Exploit
Before diving into specific techniques, it is worth being clear about what confirmed means here. A CL.TE or TE.CL condition on its own is a parsing disagreement interesting, but not yet a finding with business impact. Exploitation is the process of using that disagreement to do something that actually violates a security boundary reading data you should not see, writing data you should not be able to write, or impersonating a request you did not actually send.
This is also where report quality separates experienced testers from beginners. A report that saysI detected a timing delay consistent with CL.TE earns far less credibility and often a lower severity rating than one that saysI used the confirmed CL.TE condition to capture another simulated user's session cookie. The techniques below are what close that gap.
Technique 1HTTP Response Queue Poisoning
HTTP response queue poisoning is often the first exploitation technique testers reach for because it is the most direct proof that a desync is real and exploitable, not just a timing artifact.
The mechanism because the front end and back end disagree about how many requests have actually been sent down a shared connection, the back end can end up with more responses queued than the front end expects to deliver. When that happens, a response meant for request #2 gets handed to the client who sent request #1 and so on down the line every subsequent response on that connection shifts by one.
In practice, this is demonstrated by sending a crafted smuggling request, followed immediately by an apparently unrelated, normallooking request. If the normal request comes back with a response that does not match what was asked for an error for a method that was never sent, or content belonging to a different endpoint that's queue poisoning in action and it is strong, demonstrable evidence for a report. It's also the foundation that most of the higher impact techniques below are built on top of.
Technique Bypassing FrontEnd Access Controls
Front ends frequently do more than just forward traffic. They often enforce path restrictions (blocking direct access to /admin unless a header is present), strip or add authentication headers, or apply a web application firewall's rule set before a request ever reaches the application layer.
HTTP Request Smuggling exploitation against this control model works by hiding the sensitive request inside the body of an apparently harmless one. The front end inspects and approves the outer request, the one it can see. The back end, however, splits that payload into two requests and processes the hidden, smuggled one on its own merits, without ever subjecting it to the front end's rules, because as far as the front end's logs and controls are concerned, that second request never existed.
This is one of the more severe exploitation paths because it can completely defeat defenses that an organization is otherwise relying on. A WAF rule blocking a known attack pattern, or a reverse proxy configured to only allow internal IP ranges to reach an administrative endpoint, can both be sidestepped this way not because the rule itself is flawed, but because the request bypassing it is invisible to the layer enforcing it.This progression also mirrors how most people actually get into bug bounty hunting productively with this bug class starting with detection on lower stakes scope, then gradually building toward the higher severity exploitation techniques once the mechanics are second nature.
Technique 3Session Hijacking via Smuggled Requests
This is usually the technique that earns the highest severity rating in a report, because it demonstrates direct impact against another user rather than against the system itself.
The approach an attacker smuggles a partial request targeting an endpoint that reflects or stores request data somewhere visible to the attacker: a comment field, a search history log, an error page that echoes back submitted headers, or similar. Critically, the smuggled request is left deliberately incomplete. The next legitimate visitor's request, arriving on the same reused backend connection, gets concatenated onto the end of it supplying the headers, cookies and body data needed to finish the attacker's request.
The result is that the victim's own session cookie, authorization token, or other sensitive header ends up embedded in a request the attacker constructed and if that endpoint reflects or stores what it received, the attacker can retrieve the victim's data afterward. This is the mechanism behind realworld demonstrations of stealing another user's authenticated session purely through request smuggling, with no phishing or clientside payload involved at all.
Technique 4HTTP Cache Poisoning Chains
HTTP cache poisoning through request smuggling is arguably the most scalable exploitation technique, because a single successful attack can affect every subsequent visitor to a cached URL, not just one victim.
The chain works like this: a smuggled request is crafted so that the back end's response to it, which the attacker fully controls the content of, gets associated by the caching layer with a different, legitimate, hightraffic URL. Once that poisoned entry is stored, every visitor who requests that legitimate URL receives the attacker's response instead, until the cache entry expires or is manually purged. Depending on what the attacker put in that response, this can mean serving malicious scripts, redirecting users to attacker controlled infrastructure, or simply defacing a high visibility page.What makes this technique particularly dangerous from a defender's perspective is scale without repetition the attacker only has to successfully exploit the desync once per cache entry and the caching layer does the rest of the distribution work for them.
Technique Chaining With Other Vulnerability Classes
Experienced testers rarely treat request smuggling as a standalone finding. It's frequently used as a delivery mechanism that upgrades the severity of other, lower impact bugs.
A good example is a reflected crosssite scripting issue that would normally require convincing a victim to click a specially crafted link. Delivered through a smuggled request instead, the same payload can reach a victim who simply loads a page normally, removing the social engineering step entirely and turning a required user interaction bug into one that doesn't. The same logic applies to chaining with an open redirect vulnerability on its own, an open redirect is often rated low severity, but used as the destination of a smuggled, cachepoisoned response, it can silently funnel every visitor of a trusted page to attackercontrolled infrastructure.
When you're assessing severity during an engagement, always ask what else in the application's attack surface a confirmed desync condition could be used to deliver the answer is frequently more damaging than the parsing bug on its own.
HTTP Request Splitting as a Related Primitive
HTTP request splitting is closely related terminology, sometimes used interchangeably with smuggling, though it's more precisely used to describe the act of causing a single request to be interpreted as two distinct ones by a downstream parser. In exploitation terms, this is the mechanical step that every technique above depends on; without the ability to split one request into two from the back end's perspective, none of the higher impact outcomes are reachable. Understanding request splitting as the underlying primitive, rather than a separate attack, helps when you're explaining a finding to a client who's only familiar with the broader smuggling term.
Why Exploitation Keeps Working Against Modern Stacks
A reasonable question at this point is why these techniques still succeed against actively maintained, wellfunded infrastructure. The answer is that exploitation depends on an architectural condition of two different HTTP parsers sitting in the same request path rather than a single coding mistake that a patch can close once and for all. An organization can update its application framework, rotate its load balancer vendor, or migrate to a new CDN and each of those changes can independently reintroduce the exact parsing disagreement that makes every technique above possible again, even if the original vulnerability was fixed months earlier.
This is part of why exploitation findings in this bug class are rarely a one fix for the team receiving the report. The underlying root cause tends to sit at the boundary between infrastructure and application ownership, which is also precisely the boundary that custom internal gateways, proxies and middleware often fall into without clear review ownership. Teams that treat raw HTTP parsing and forwarding code as a routine part of their secure coding best practices review rather than infrastructure only concern tend to catch these conditions before they reach production, since the review happens at the point where the ambiguity is actually introduced.
Documenting Exploitation for a Credible Report
How you document an exploitation chain matters almost as much as finding it. A report that only states the final impact (could steal user sessions) without the reproducible request sequence that produced it is difficult for a triager or engineering team to verify and difficult for them to confirm is actually fixed later. Strong reports for this vulnerability class typically include:
The exact raw request(s) used, including header casing and line endings, since subtle formatting differences can be the entire reason the desync triggers
The specific variant confirmed (CL.TE, TE.CL, or TE.TE) and the evidence used to confirm it
A clear, numbered walkthrough from the initial smuggled request to the observed impact, written so someone unfamiliar with the bug class can follow it
Screenshots or raw response captures showing the victim facing evidence a stolen header, a poisoned cache response, or a bypassed restriction
Vague descriptions are the single biggest reason otherwise valid request smuggling reports get downgraded or sent back for clarification during triage.
Tooling for Exploitation, Not Just Detection
Detection tooling (covered in depth in our dedicated testing and detection guide) gets you to a confirmed vulnerability. Exploitation typically requires more manual, fine grained control over raw requests than most general purpose scanners provide. A request crafting tool that lets you control exact byte sequences, disable automatic ContentLength recalculation and send requests with precise timing is nonnegotiable at this stage automatic helpers built into many HTTP clients will silently repair the exact malformation your exploit depends on.
It's also worth building exploitation muscle memory in a safe environment before attempting any of these techniques against a live target. This is one of the clearest cases where structured lab practice outperforms reading alone, since the exact chunk sizes, byte offsets and header formatting required are genuinely fiddly to get right by hand the first several times.
Building This Skill Set Methodically
If you're relatively new to this vulnerability class, it's worth sequencing your learning rather than jumping straight to the most advanced exploitation technique. A structured path working through a beginner CTF roadmap first, then progressing into dedicated web application CTF challenges that include smuggling specific scenarios builds the raw protocol comfort you need before attempting session hijacking or cache poisoning chains against anything resembling a real target.Trying to skip straight to session hijacking against a production target, without that foundation, is where most costly testing mistakes happen.
Rigorous testers also fold this bug class into their standard process by referencing the OWASP Web Security Testing Guide, which treats it as a distinct, named test case rather than something to stumble into accidentally and by keeping threat modeling conversations in view when deciding how aggressively to pursue exploitation on a given engagement, since the blast radius of techniques like cache poisoning extends well beyond the specific endpoint being tested.
Conclusion
Exploitation is where HTTP Request Smuggling Techniques stop being an interesting protocol curiosity and start being a genuine security risk worth a client attention. Response queue poisoning gets you proof. Access control bypass, session hijacking and cache poisoning chains get you an impact. And chaining the technique with other vulnerability classes is often where the real severity lives. Build this skill methodically, in a lab environment, before ever applying it against a live target and when you're ready for the complete reference covering every variant and defense alongside these techniques, our full HTTP Request Smuggling Attack guide ties it all together. AppSecMaster offers handson labs built specifically for practicing this exploitation chain safely.
Frequently Asked Questions (FAQs)
What is the difference between detecting and exploiting an HTTP Request Smuggling Vulnerability?
Detection confirms the underlying parsing disagreement exists, usually through a timingbased probe. Exploitation uses that confirmed condition to demonstrate actual impact of stolen session data, bypassed access controls, or a poisoned cache entry which is what turns a theoretical finding into a reportable, high severity issue.
Which exploitation technique is considered the most severe?
Session hijacking and cache poisoning chains are typically rated highest, because both demonstrate direct impact against other users or at scale, rather than against the vulnerable system in isolation. Access control bypass is also serious when it exposes administrative functionality.
Do I need to test CL.TE, TE.CL and TE.TE separately during exploitation?
Yes. Each variant produces a different desync behavior and requires a differently structured payload to exploit reliably. Confirming one variant doesn't rule out or confirm the others and the order in which you test them matters, since a probe for one orientation can disrupt the connection state needed to test the other.
Can these exploitation techniques be automated end to end?
Detection can be largely automated. Exploitation generally can't be, at least not reliably, because it depends on target specific details which endpoint reflects data usefully, what the cache key normalization logic looks like and how the application handles partial or malformed input. Manual, iterative testing is still the norm here.
Is it safe to practice these exploitation techniques myself?
Only against systems you own, have explicit written authorization to test, or that are purpose built vulnerable labs. Because these techniques frequently rely on shared, reused backend connections, exploitation attempts can affect other real users if run against production systems without authorization; this is not a vulnerability class to experiment with casually.